A California platform now removes people from the data-broker supply on a 45-day cycle. The buyer of that data receives no notification of any kind — only a match rate that is quietly worse than it was last quarter.
On 1 August, the operative deadline under California's DELETE Act arrived: registered data brokers must begin processing consumer deletion requests submitted through DROP, the Delete Request and Opt-out Platform run by the California Privacy Protection Agency.
The mechanism is worth understanding precisely, because it is unlike every other privacy obligation marketing teams have absorbed. This one does not ask you to do anything. It removes things from your suppliers, continuously, without telling you.
How the pipeline works
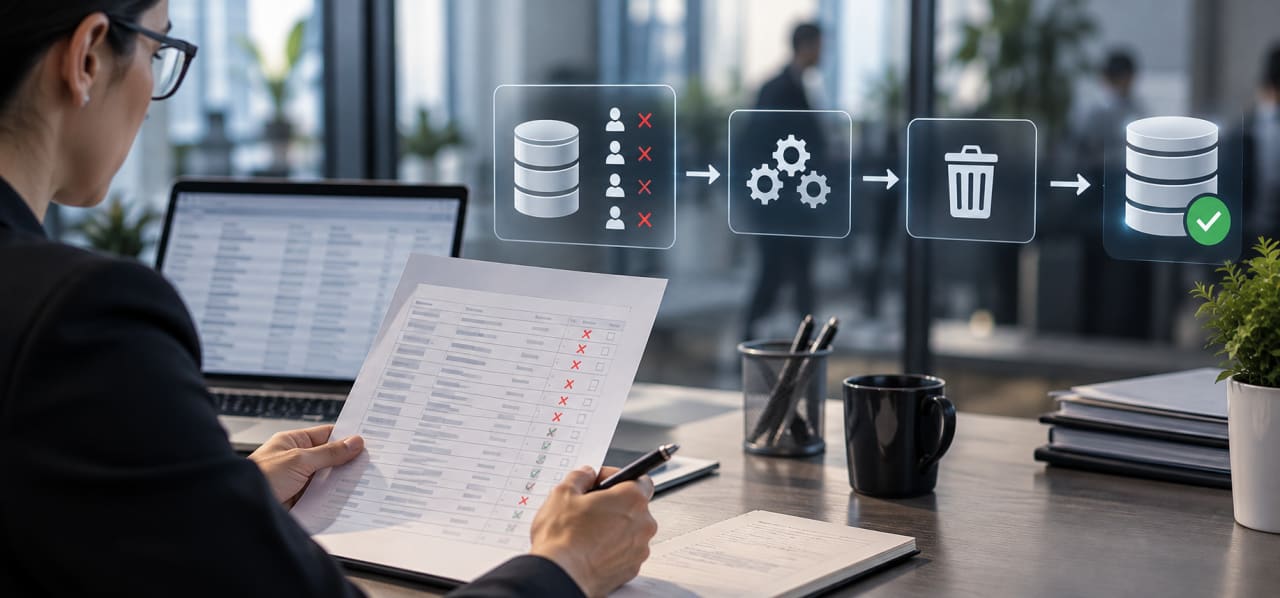
A California resident submits a single deletion request to the state platform rather than to individual companies. Every registered data broker — there are more than six hundred — must check DROP at least once every forty-five days, retrieve the list of requesters, match it against their own holdings, and delete the personal information of anyone who matches. Access is by CSV download or API. Under SB 361, the penalty for failing to register or comply is $200 per consumer, per day, which compounds fast enough that compliance is the only rational posture for anyone actually registered.
There is no notification to downstream buyers. There is no flag on the affected record in a data feed. A person is simply present in the file one cycle and absent the next.
Every previous privacy regime changed what marketing was permitted to do. This one changes what the supply contains, on a schedule, silently.
What it looks like from inside marketing operations
Not like a compliance event. Like a data-quality problem with no obvious cause.
The symptoms are ordinary enough to be misattributed. An enrichment vendor's coverage on California accounts slips a few points. A suppression or match job returns fewer hits than the same job did in the spring. An ABM audience built in March activates smaller in September without anyone changing its definition. A contact record that previously carried a direct dial now carries only a company line.
Each of those reads as vendor quality, and the usual response is to raise it with the vendor, run a bake-off against a competitor, or renegotiate at renewal. In some proportion of cases the vendor is doing exactly what the law requires and the competitor is subject to the same pipeline.
Figure 1
What you observe | Usual explanation | What may actually be happening | Where to look |
|---|---|---|---|
Enrichment coverage drops on a region | Vendor data quality declining | Deleted records leaving the supplier's holdings | Coverage by state over time, California against a control region |
A saved audience shrinks without a definition change | Platform bug or filter drift | Underlying records removed upstream | Audience size history against sweep timing |
Match rates fall in roughly regular steps | Random variance | A 45-day sweep cadence expressing itself | Plot match rate by month, not by campaign |
Contact detail thins on existing records | Record ageing | Partial deletion of matched personal information | Field-level completeness, not record counts |
The tell is the rhythm. Ordinary data decay is gradual and unstructured; a mandated sweep cycle produces a repeating step pattern.
Why B2B teams assumed this was not their problem
Because the DELETE Act is discussed as a consumer-privacy measure, and B2B marketers have grown used to a working assumption that business contact data occupies a softer category. Under California law it does not in the way that assumption implies — a named individual at a company is a consumer whose personal information is personal information, and the business-purpose carve-outs that once cushioned B2B have narrowed considerably.
The practical consequence is that a substantial share of the third-party B2B supply — intent providers, enrichment vendors, list brokers, some ABM platforms whose audience graphs are built on purchased data — sits either inside the registered-broker population or downstream of it.
What to actually do
Establish which of your data suppliers are registered brokers.The California register is public. Any supplier of third-party audience, intent or contact data that is not on it is making an implicit claim about its data sourcing that is worth asking about directly.
Ask each supplier the operational question, not the compliance one.Not "are you compliant" — everyone says yes — but how often they sweep, when their last sweep ran, and whether they can report deletion volumes affecting your subscribed segments.
Instrument coverage by geography before you need to.A California-versus-control-region coverage series makes this visible in a quarter. Without a baseline, you cannot separate this from ordinary decay.
Stop treating match rate as a vendor scorecard in isolation.If every supplier in a category is subject to the same pipeline, a bake-off measures which vendor swept most recently rather than which holds better data.
Put a sweep-disclosure clause into the next renewal.Not deletion volumes at record level, which no broker will give you, but a commitment to notify on material coverage change in a subscribed segment. It costs nothing to ask for at renewal and is unobtainable mid-term.
The direction of travel
The significant thing about DROP is not its current reach. It is the design: a single state-operated point at which a person can withdraw from an entire supply chain, with a compounding daily penalty behind it and a machine-readable interface in front of it. That is a template, and templates of this kind rarely stay in one jurisdiction.
For teams whose demand model rests on purchased audience, the planning assumption worth adopting now is that third-party coverage becomes a declining asset with a maintenance cost, rather than a stable input that occasionally needs refreshing. That is a budgeting conclusion as much as a privacy one, and it is better reached deliberately than discovered through a match rate.
Sources and notes. California's DELETE Act and the Delete Request and Opt-out Platform (DROP), operated by the California Privacy Protection Agency, with broker deletion-processing obligations operative from 1 August 2026; brokers must access DROP at least every 45 days via CSV or API; SB 361 sets a penalty of $200 per consumer per day for non-compliance; more than 600 data brokers are registered. Compiled from published compliance guidance; we have not independently verified request volumes and have deliberately omitted circulating figures we could not trace to a CPPA source. The observational patterns in Figure 1 are analytical, not measured. Journalism, not legal advice. Corrections welcome.